
Monitoring and audit
See how the site is running, who did what, and what was refused.
Diagnostics
The pages under Diagnostics are open to system administrators, administrators and auditors. Those marked site cover the whole site and need a global administrator.
| Page | Shows |
|---|---|
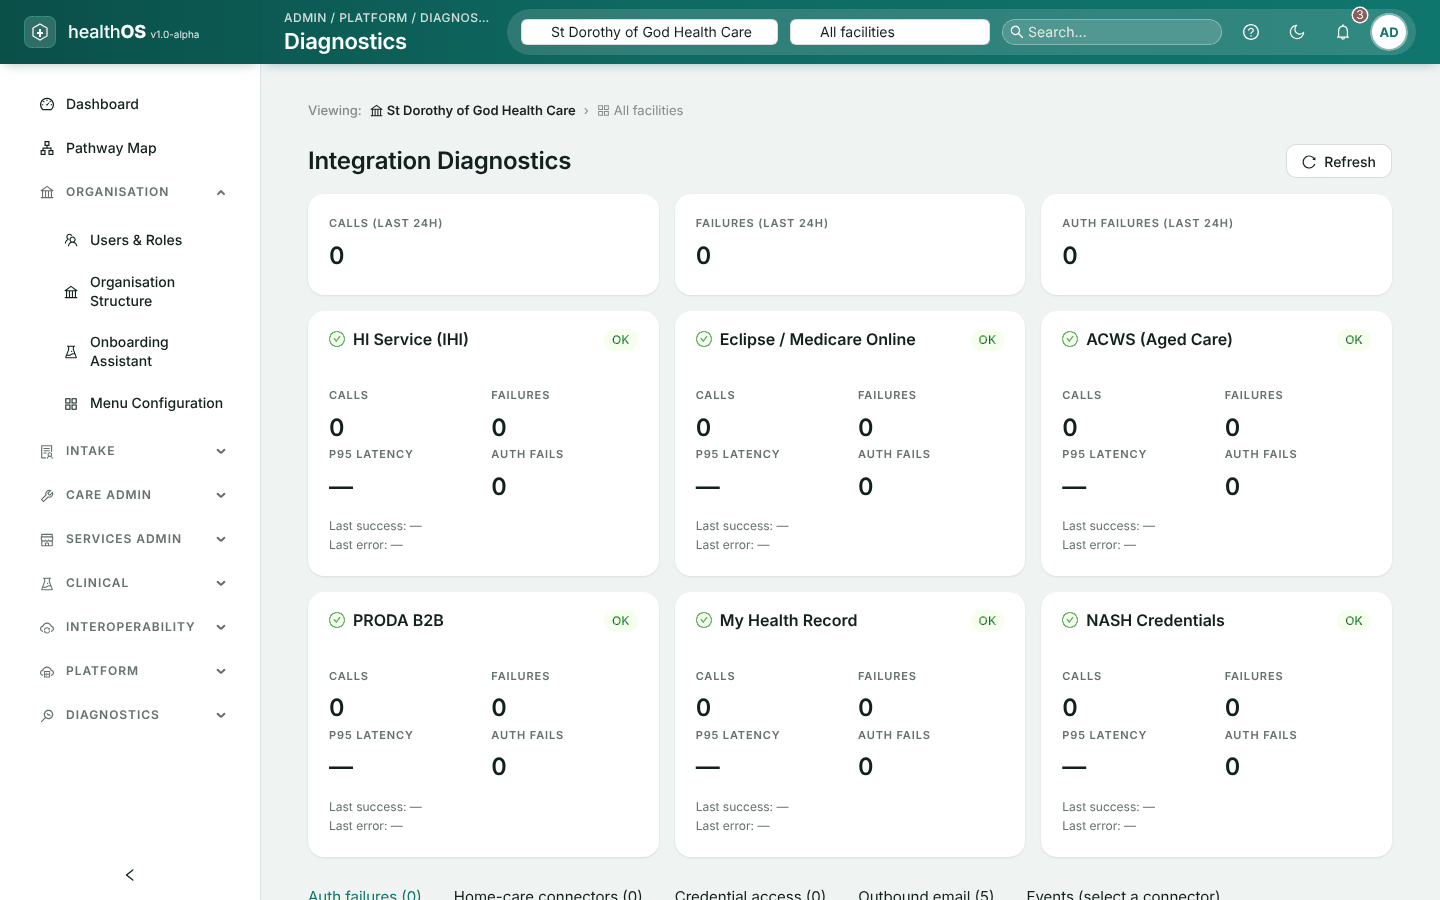
| Health | Calls, failures and sign-in failures over the last day for each government service: the HI Service, Medicare Online, ACWS, PRODA, My Health Record and NASH |
| Logs (site) | A live view of the service logs, with personal details removed |
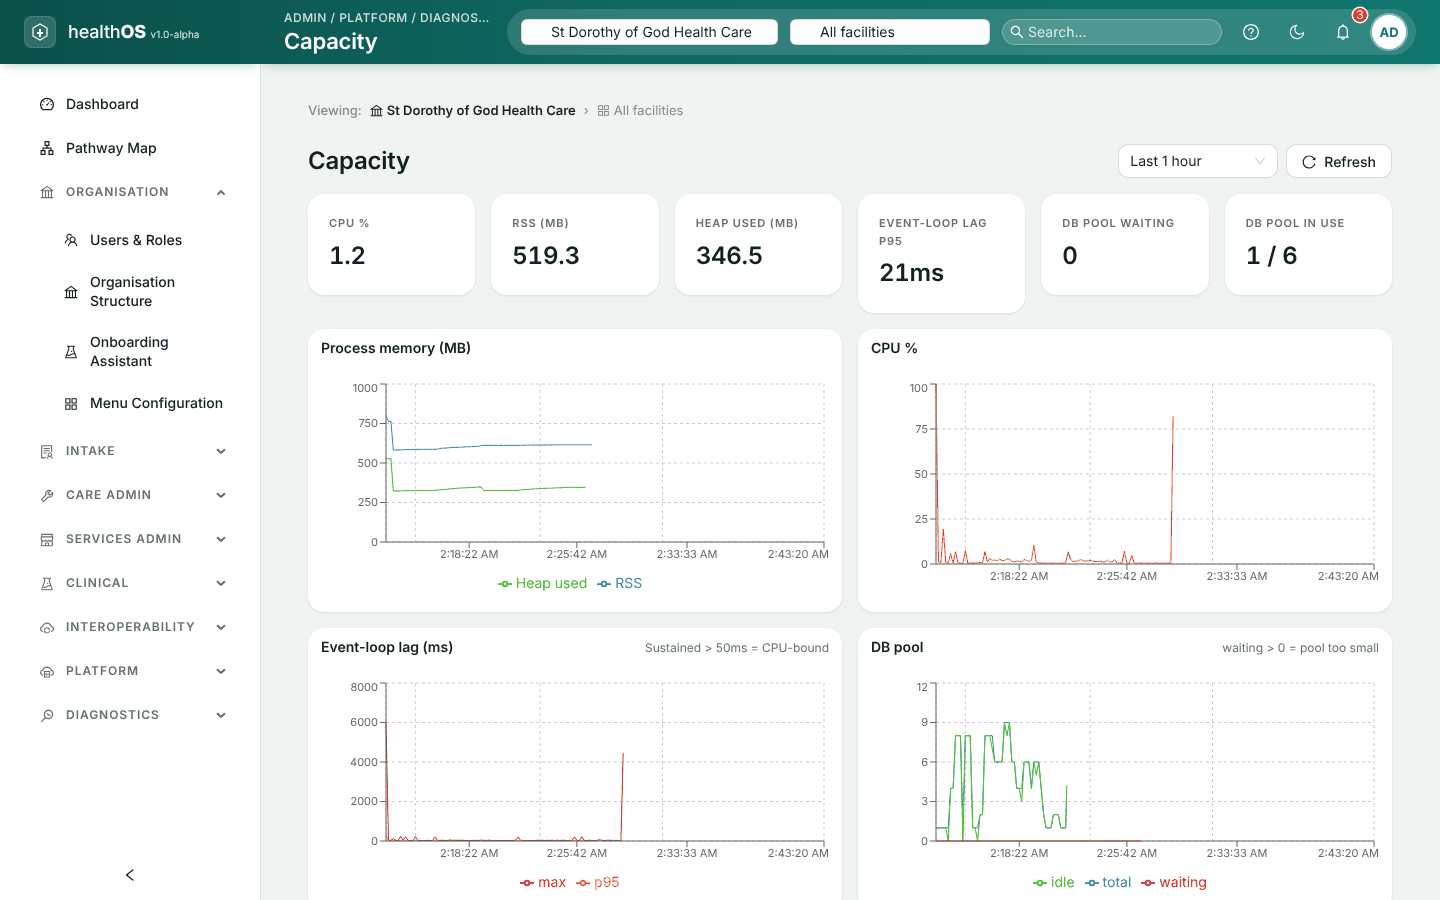
| Capacity (site) | Processor, memory, responsiveness and database use |
| Database (site) | A direct view of the database. Changes made here skip HealthOS’s own checks, so use it only when nothing else will do, and record why. |
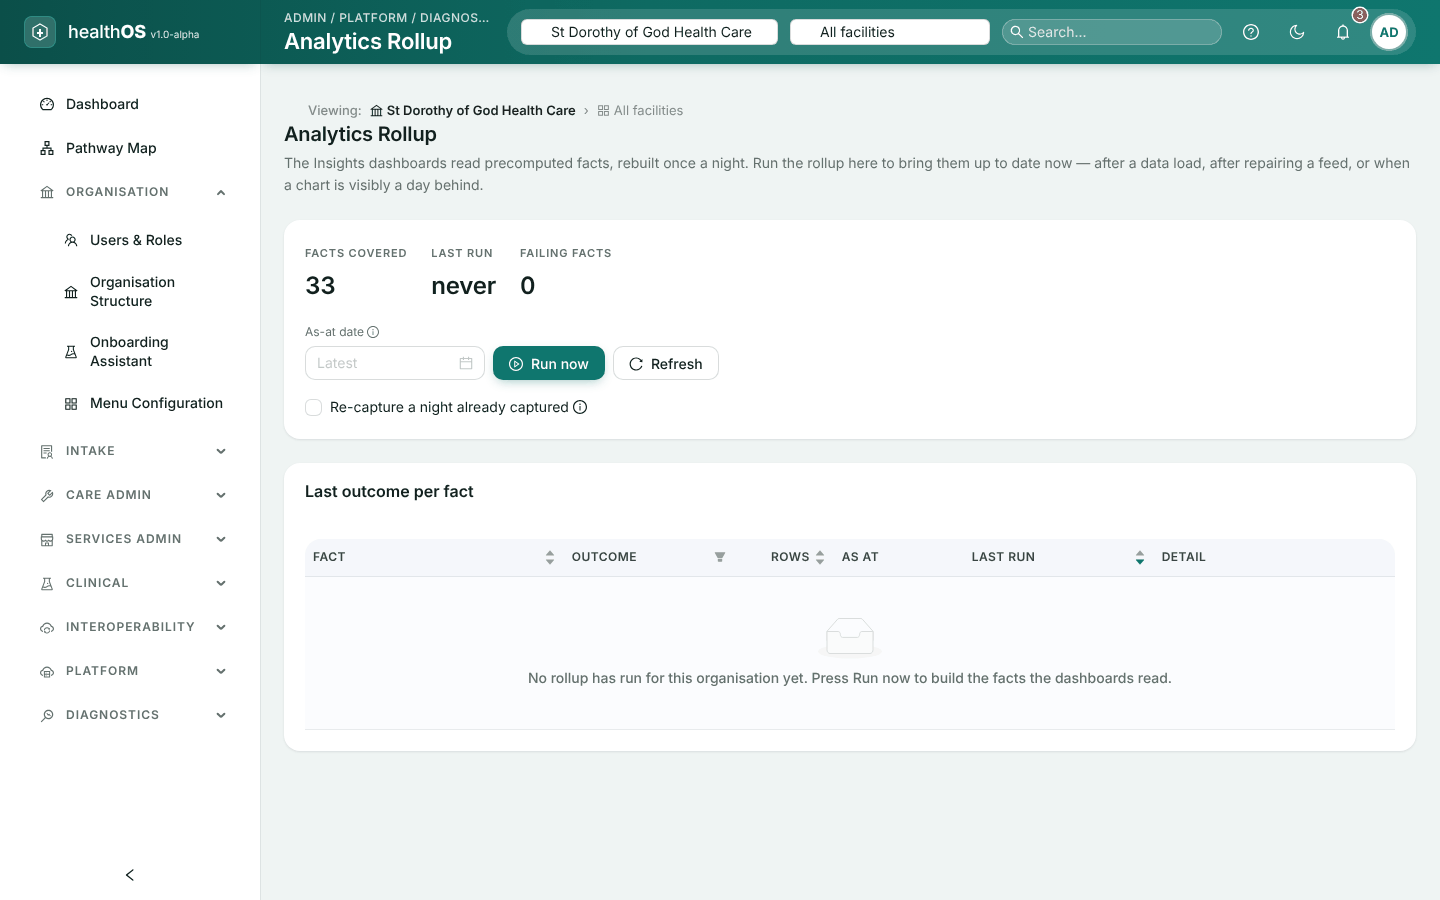
| Analytics Rollup | Whether last night’s reporting refresh ran, and Run now |
Audit trails
Audit records cannot be changed or deleted, by anyone, and are kept for seven years. Recording them never holds up the work being recorded.
| What | Where to read it |
|---|---|
| Sign-ins, lockouts, two-step sign-in and password changes | Organisation › Users & Roles › Auth Events, with export |
| Changes to records, and corrections | The audit view of each record |
| Setting changes | The history on each part of the organisation tree |
| Licence changes | Platform › Tenant Licensing › History |
| Entra provisioning | Authentication & Identity › Staff Apps |
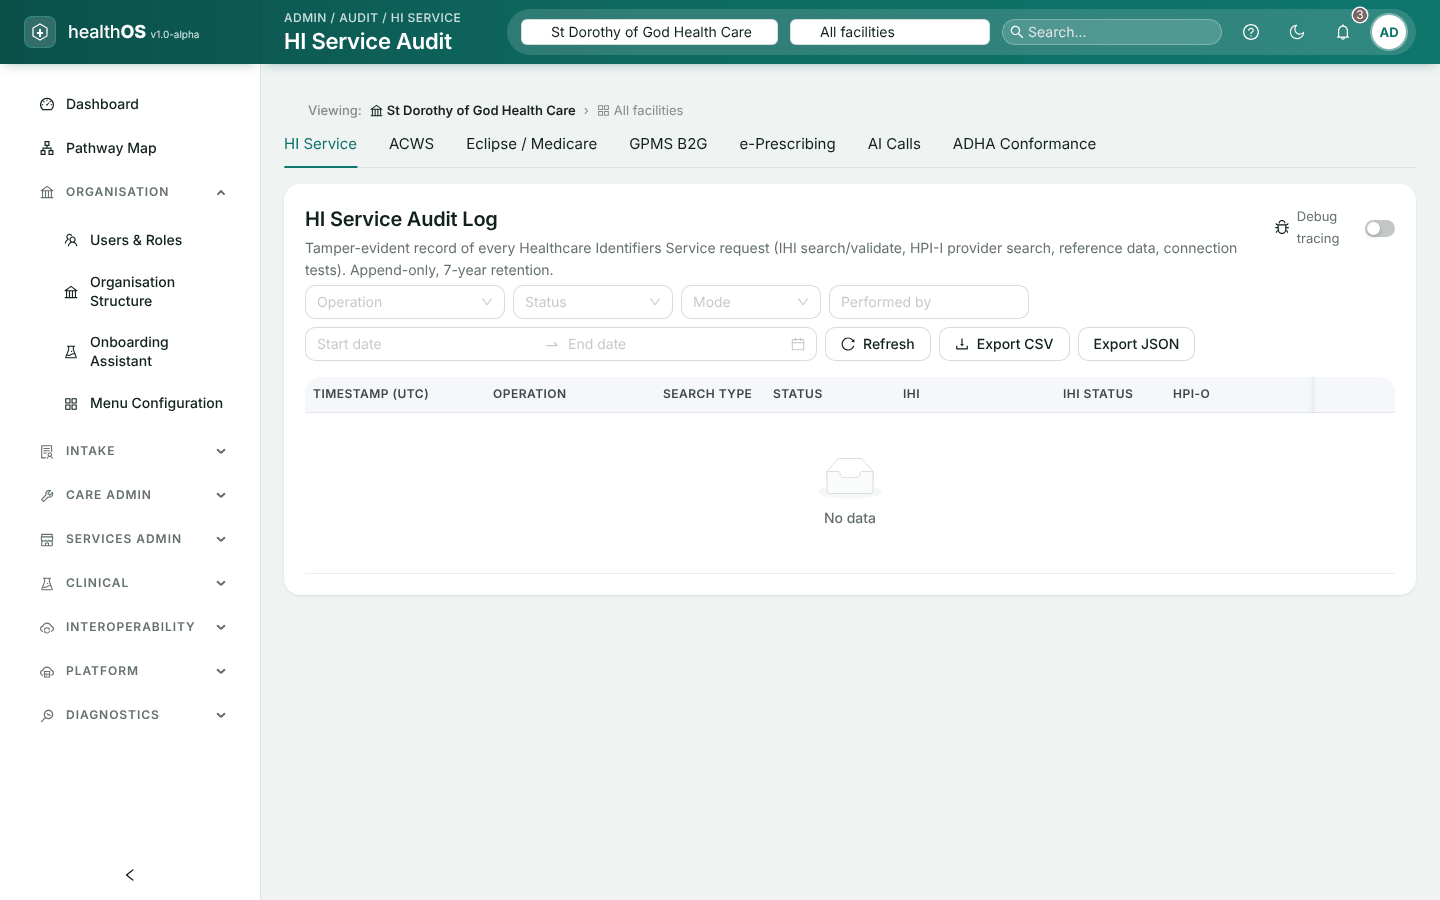
| Government services and AI | Interoperability › Audit, with a tab each for the HI Service, ACWS, Medicare Online, GPMS, electronic prescribing, AI requests and My Health Record conformance. Each can be filtered and exported. |
The AI requests tab shows the questions sent to the AI and its answers, which include health information. Give the auditor role only to people entitled to see it.
Security events
HealthOS records every refused attempt to reach another organisation’s data or to misuse a sign-in token. Examples:
- a request naming an organisation the person does not belong to;
- a token used with the wrong service;
- a webhook that failed its signature check;
- a sign-in response that failed its checks.
Repeated attempts from one source are grouped by the minute. A global administrator can search them by kind, organisation, address, person and time. Each event is also written to the logs, so your monitoring can raise an alert on it.
A routine checklist
| How often | Check |
|---|---|
| Daily | Diagnostics › Health for failing government services. Integration Flows for held or failed messages. |
| Weekly | Security events. Auth Events for lockouts and breached-password alerts. |
| Monthly | Accounts disabled as dormant. Grants about to end. Connector licences near their end date. The PRODA device’s key expiry (HealthOS warns 30 days ahead). |
| Quarterly | Who holds the system administrator, administrator and auditor roles, and whether they still should. |
Still stuck? Email support@healthos.net.au